Everything the panel does, from a script or your assistant
A REST API and an MCP server on the same tokens. Read-only when that is all a job needs, and never more than the person who made the token can do.
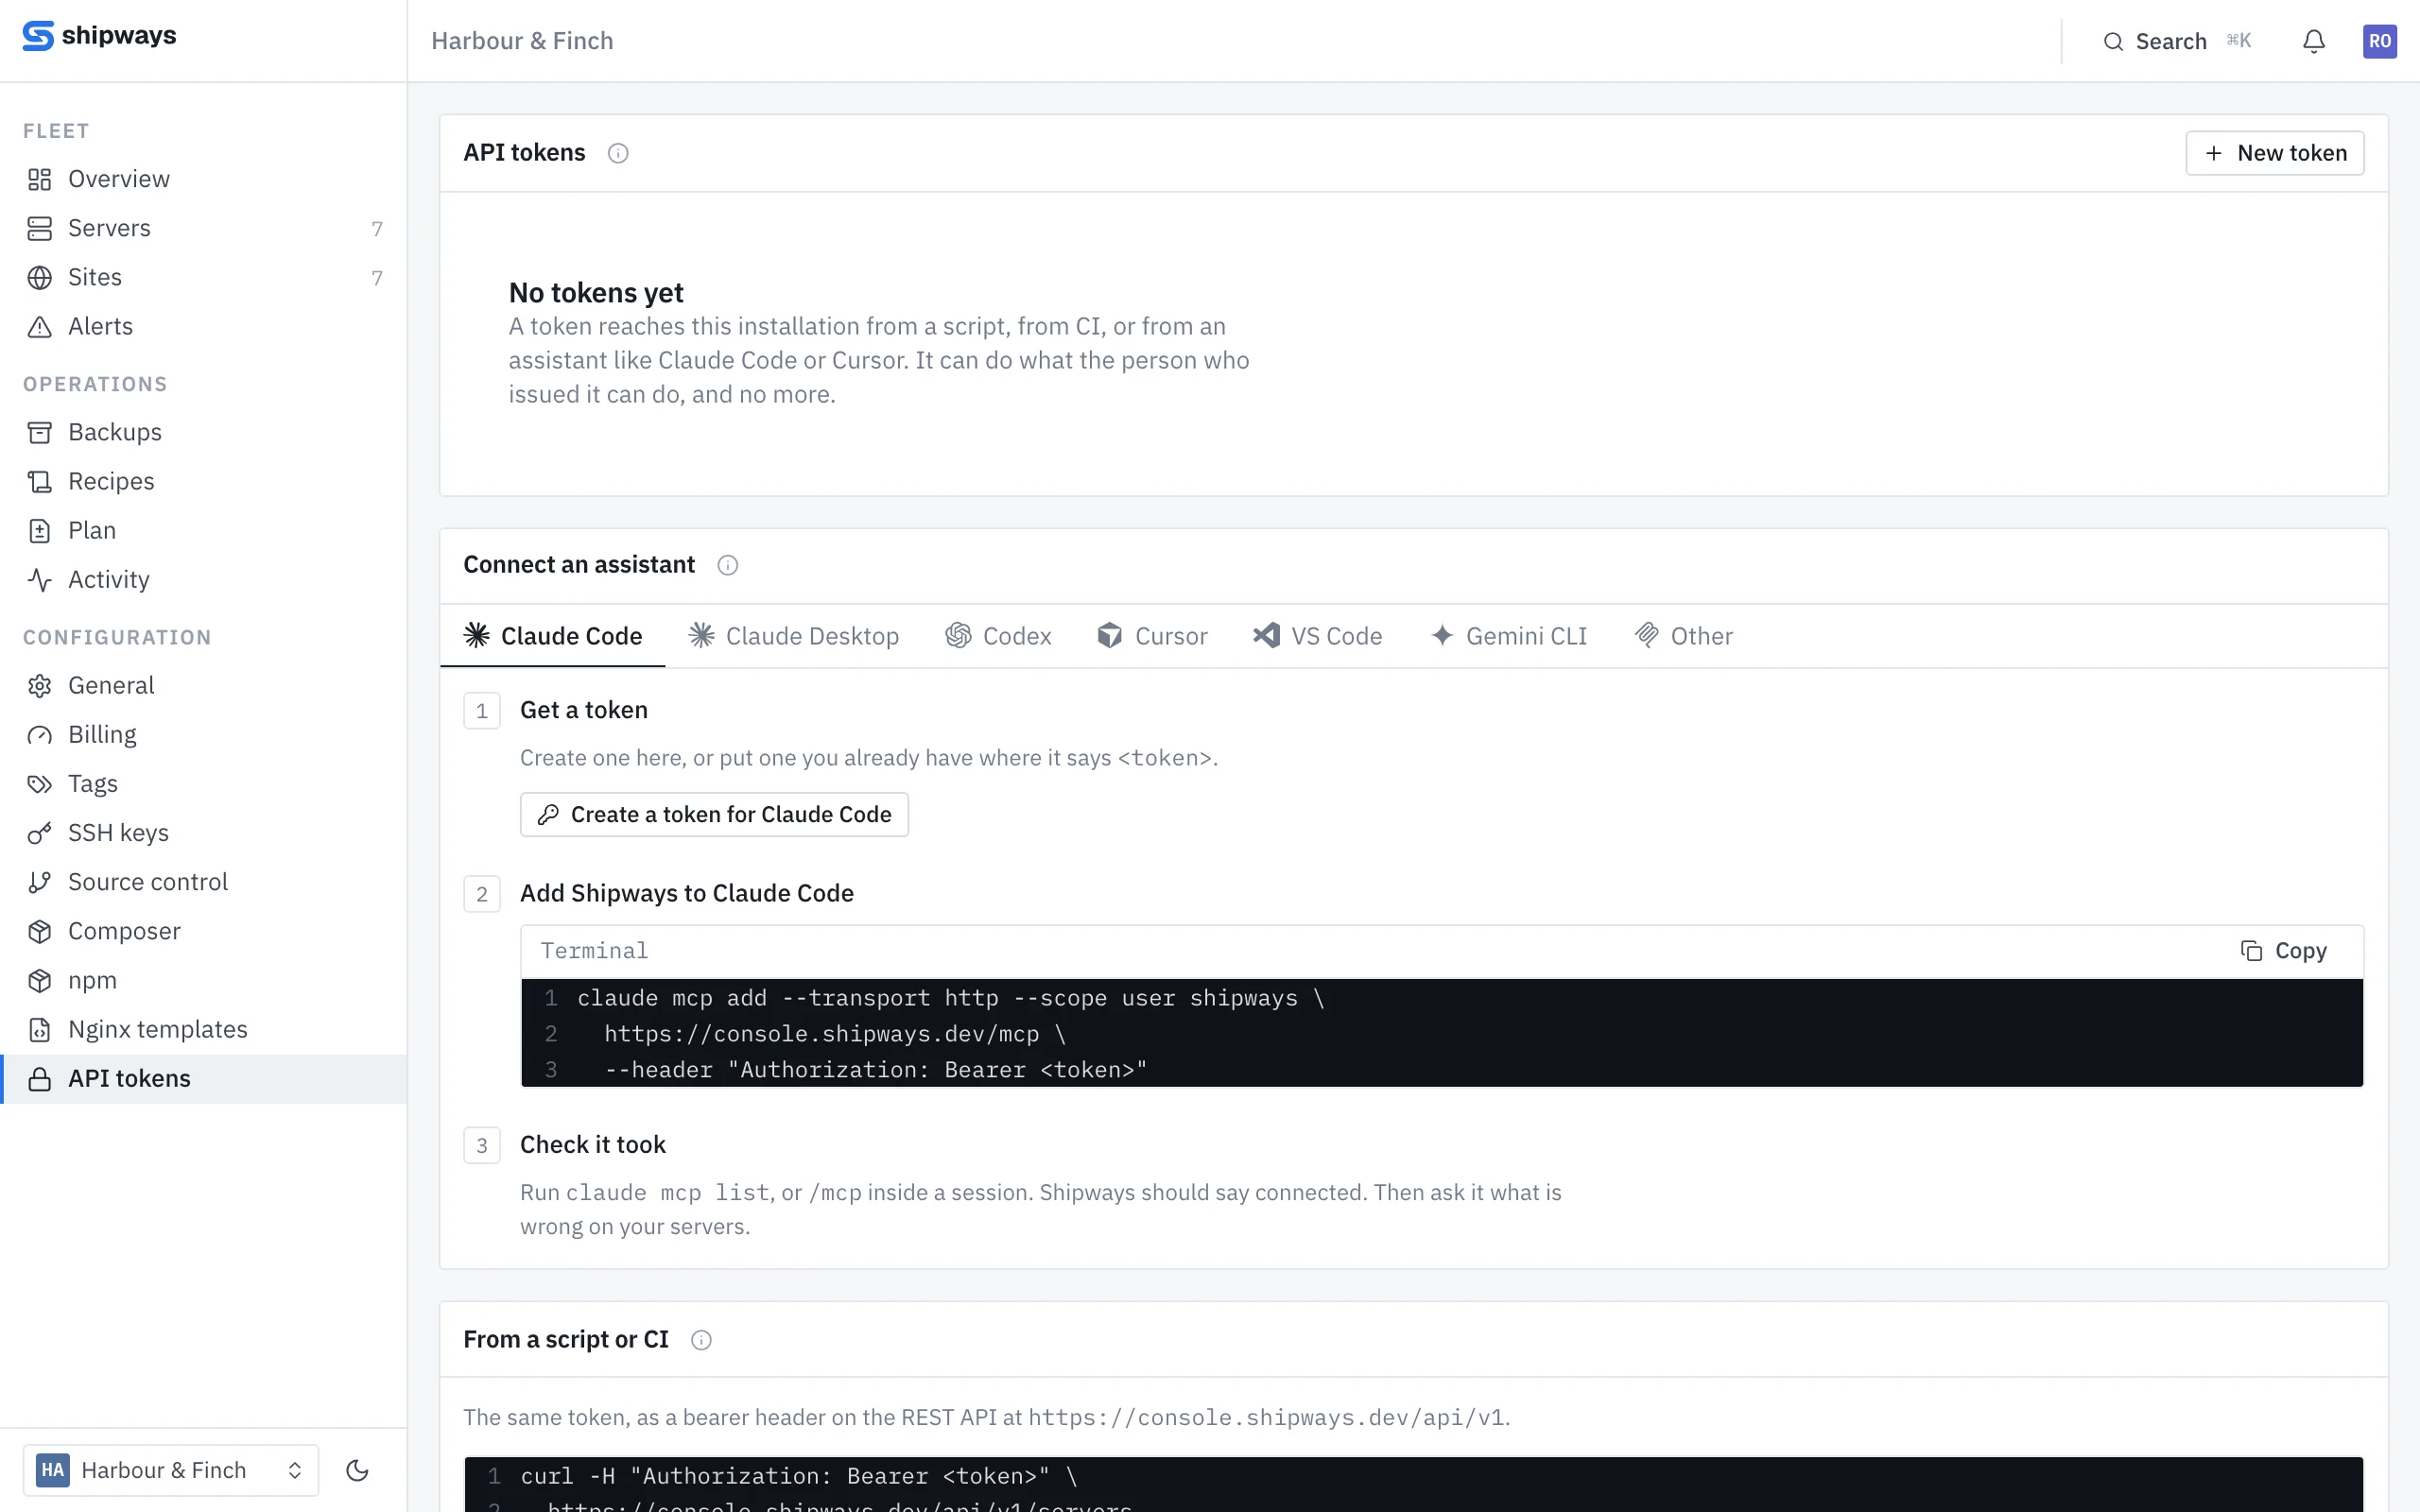
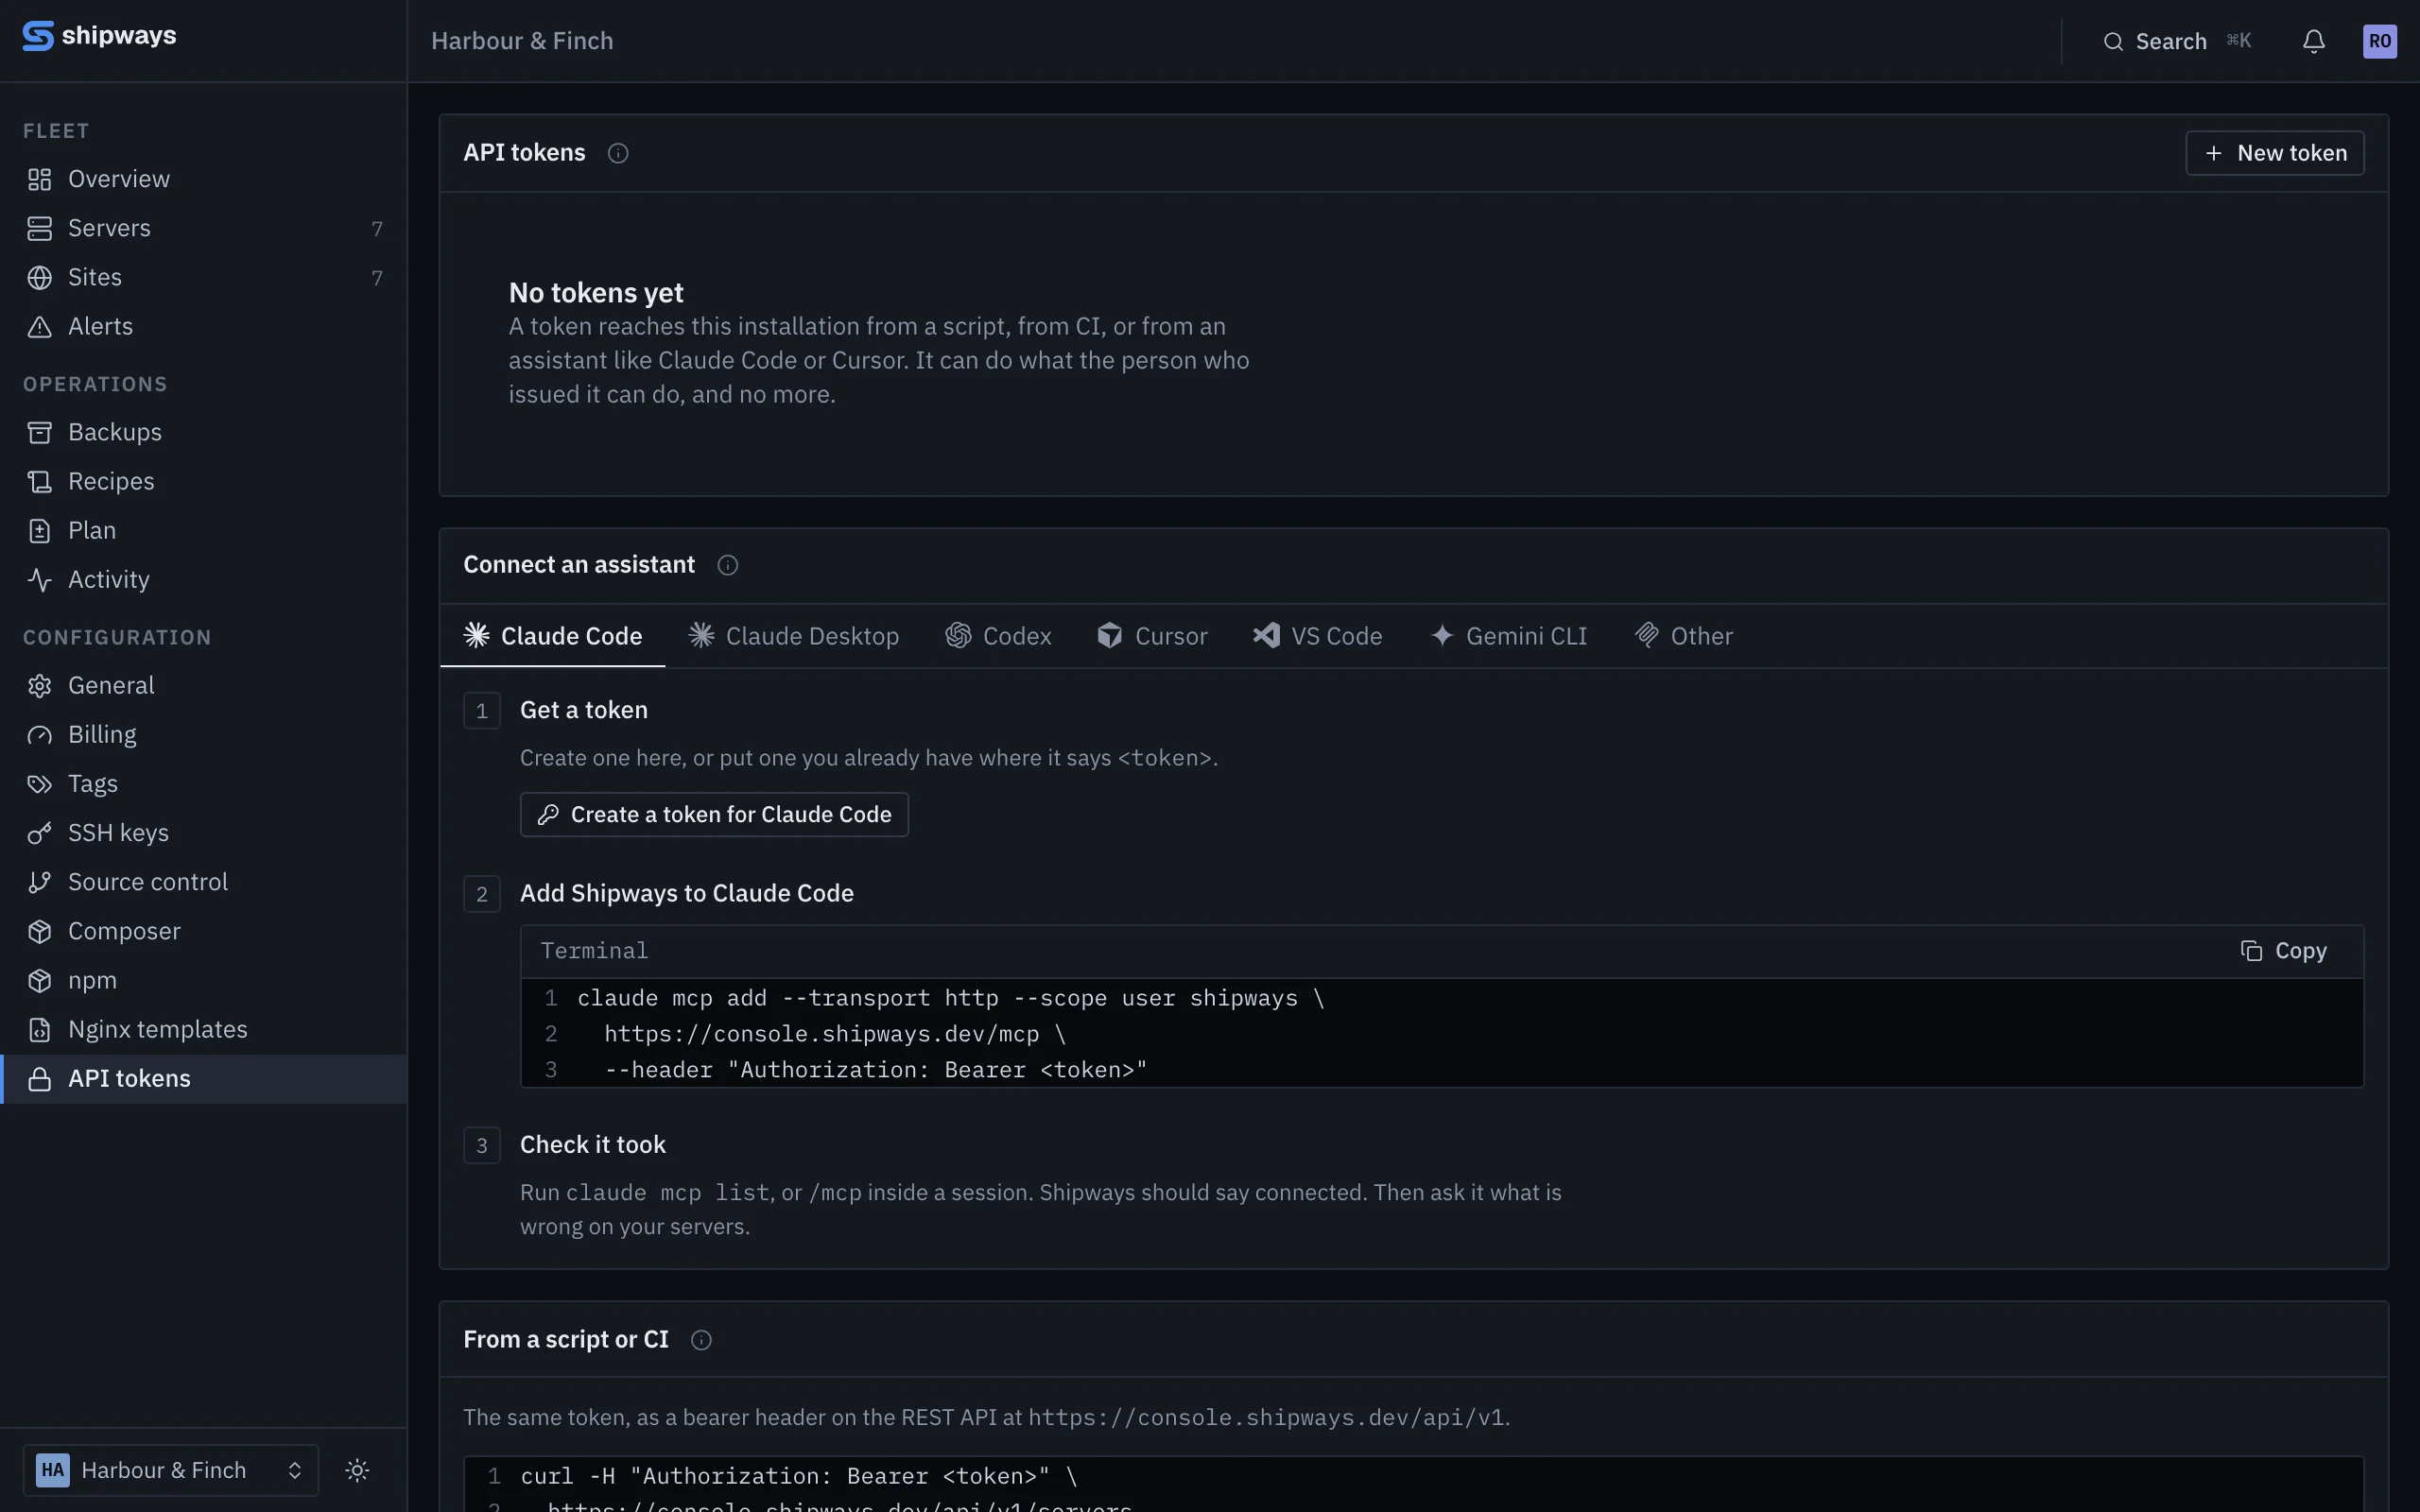
Your assistant can deploy, and read why it failed
The MCP server lists servers, sites, deployments, databases, daemons and alerts. It deploys a site and follows the deployment, reads any step's log with secrets redacted, restarts a daemon, turns on the scheduler, and changes one line of an environment file by sending the whole file back with what it read.
- Setup generated for Claude Code, Claude Desktop, Codex, Cursor, VS Code and Gemini CLI
- One-click install for Cursor and VS Code
- Every change, and reading .env, needs a token that can write
# add Shipways to Claude Code
claude mcp add --transport http --scope user shipways \
  https://console.shipways.dev/mcp \
  --header "Authorization: Bearer <token>"

# then ask
> the last deploy of harbourfinch.com failed. why?

  deployment-status  failed at "Check the release can boot"
  deployment-log     Class "App\Providers\NewsletterServiceProvider" not found
The same objects, at /api/v1
Servers, sites, deployments, databases and their users, daemons, scheduled jobs, certificates and alerts.
Anything that changes a machine answers 202 with a task id, because the
work is queued, not done, by the time the request returns.
- Tokens carry the organization, so there is none to pass
- 120 requests a minute per token by default
- Expiring after 30 days, 90 days, a year, or never; revoked at once
curl -X POST \
  -H "Authorization: Bearer $SHIPWAYS_TOKEN" \
  https://console.shipways.dev/api/v1/sites/42/deployments

HTTP/1.1 202 Accepted
The plan on every pull request
Send the plan endpoint a branch, or a shipways.yaml you are still writing, with a read token and get
back every change a deploy of it would make. A file a deploy would stop on is a 422
with the line of each problem, so a pipeline can fail before anything merges.
- name: Plan shipways.yaml
  run: |
    curl -fsS https://console.shipways.dev/api/v1/sites/42/spec/plan \
      -H "Authorization: Bearer ${{ secrets.SHIPWAYS_TOKEN }}" \
      -d ref="$GITHUB_HEAD_REF"
One machine, free, for as long as you like
No card and no end date. Connect a spare box and watch it provision; everything it builds carries into whichever plan you move to.